User Authentication via an External Identity Provider (IdP)
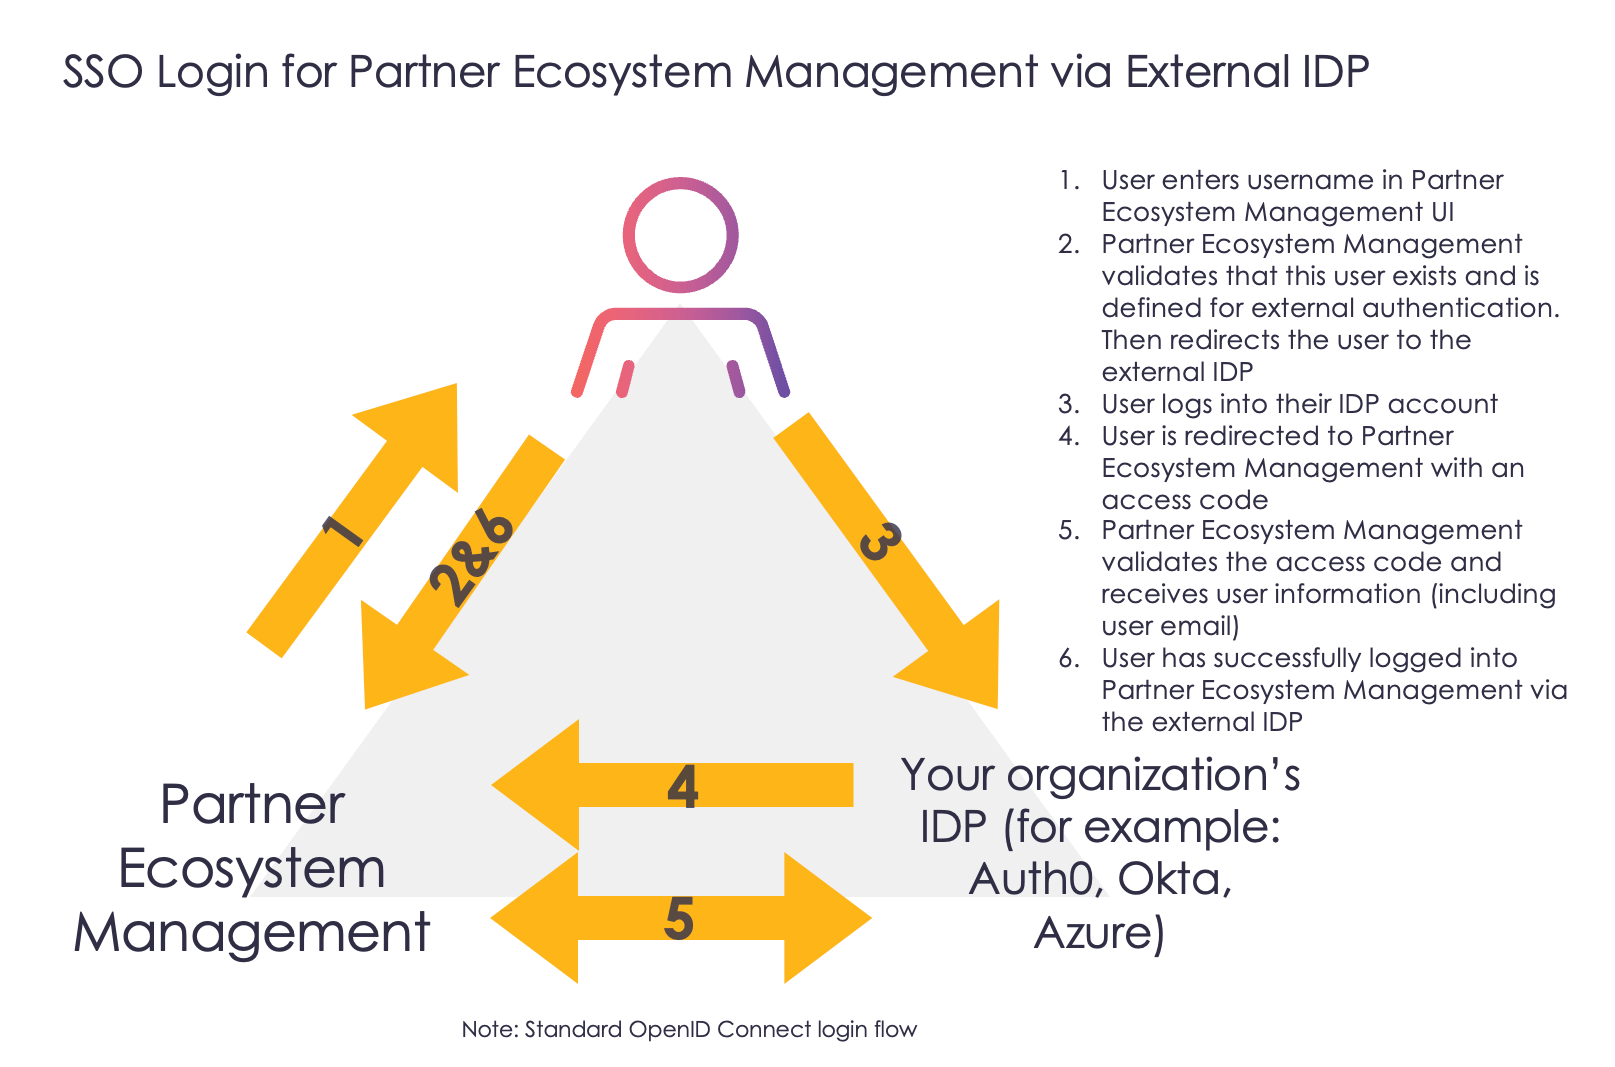
Partner Ecosystem Management supports external identity provider (IdP) federation. Organizations can use their own external IdPs for user authentication. Users can leverage the same credentials that they already use for the external IdP. When users are already authenticated with their IdP, they don’t have to log in again to access Partner Ecosystem Management. Once authenticated, users permissions to view and access different areas are based on their authorized user role.
By default, Partner Ecosystem Management user authentication is performed natively using its own internal IdP that meets SAS70 security requirements and password complexity standards.
Optionally, Reseller (Service Provider) organizations can request to use their own external user authentication via their Identity Provider using OIDC-standards.
Once the external user authentication single sign on is set up, the users can use their external IdP credentials to access the Partner Ecosystem Management UI.