- a single API or step like the Activate User (and User Attribute) Process that verifies a user’s email or mobile.
- a multi-step process such as the Accept or Decline Service Invitation Process that requires more information from the user. Upon acceptance of the invite, the user is directed through the required steps to complete their onboarding.
Token Issuance & Redemption
There are two methods on how action tokens are issued and redeemed:- A long-form, clickable verification link that includes a redirect URL and the actual token value (appended to the end of the URL string). Once the user clicks this link, the redirect URL should navigate back to the client application, and the application provides that token value in this API request URL.
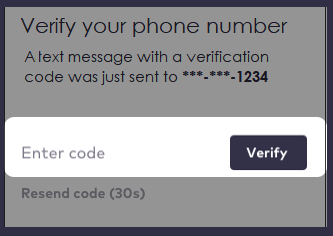
- A short-form, custom One-time Passcode (OTP) that represents the token value stored in Storefront Gateway. The user must manually supply the OTP to a Process through the application UI, and the UI must then supply both the OTP and its corresponding PKAT in this API request URL.
API URLs
GET https://{your.tenant.url}/session/token?token={**token**}GET https://{your/tenant.url}/session/token?customToken={**OTP**}&pkat={**PKAT**}
Request Parameters
Related Processes
The following Processes are invoked using the Session Token API:- Activate User (and User Attribute) Process
- Recover ID & Reset Password Processes
- Accept or Decline Service Invitation Process