Multiple Process Orchestration
Many user journeys are facilitated by a single Process. Conversely, there are some cases where Storefront Gateway orchestrates and links two or more Processes to complete a given journey.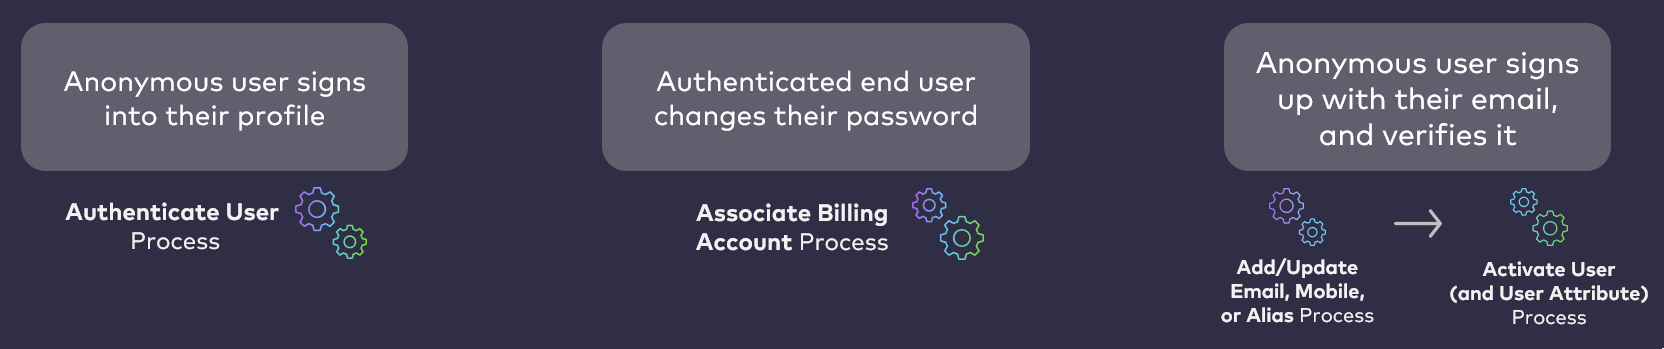
Storefront Gateway User Entity and AuthN ID Status
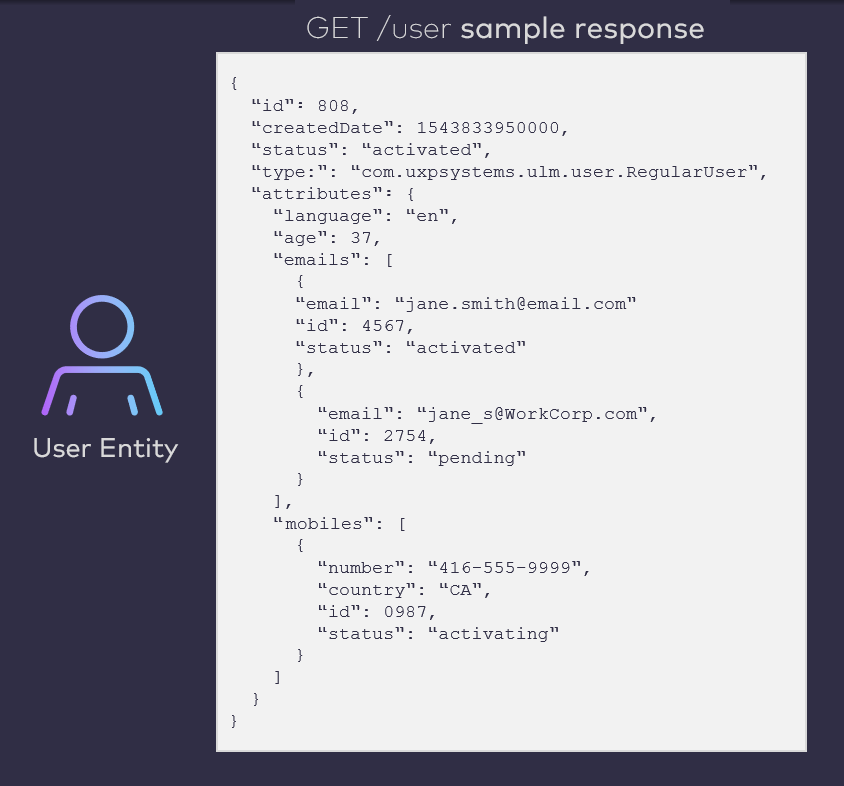
Storefront Gateway is built on top of a user-centric and entitlement-specific data model of Storefront Gateway data entities. Each Storefront Gateway entity is composed of properties and attributes, or data field names and their respective values. Each entity includes a set of default properties shared across each entity type, and anattributes property that contains additional entity-specific metadata.
End users are represented by the User entity that is defined by, among other properties, a status. The user’s registered emails and mobile numbers are stored one level down inside the attributes property, and each individual email or mobile has its own status.
Process Invocation
Unlike most Storefront Gateway Processes, Activate User is not invoked with the Process Start API. Instead, your client leverages the Session Token API. This API redeems an action token that Storefront Gateway issued at the end of a previous Process. Successfully redeeming the token causes Storefront Gateway to start (and complete) the Activate User Process. Storefront Gateway knows what entity (and what fields) to update based on context stored in the token. There are two methods to call the Session Token API in order to start a Process. Each method is appropriate to the type of notification the user receives, either a clickable verification link, or a short code that the user needs to give to the UI:- The user completes a Process.
- Storefront Gateway issues an action token, and sends a verification link in an email or SMS. The link is composed of a redirect URL back to your client application, and the full, actual token string is appended to the end of that URL.
- Once the user clicks/taps the link, they are redirected back to the client.
- The client automatically takes the token value directly from the URL, and uses it to call
GET /session/token?token={**token**}API. If the token is valid, then this triggers the Activate User Process.
- The user completes a Process.
- Storefront Gateway sends a short, custom One-time Passcode (OTP) in an email or SMS. Storefront Gateway also returns a PKAT to the client.
- The client prompts the user to enter the OTP that was sent to them.
- The user retrieves the code, and enters it into the client.
- Once the user enters their code, the client then takes the OTP and the PKAT to call
GET /session/token?customToken={**otp**}&pkat{**pkat**}API. If both the OTP and PKAT are valid, then this triggers the Activate User Process.
Common Use Cases
These are the common use cases that involve the Activate User Process:- A new, anonymous user onboards with their email or mobile . They then verify their email/mobile. This activates both the User entity and the email/mobile that is stored on the User entity as an attribute.
- A new, anonymous user onboards with their social account. However, they change the email/mobile returned by the social provider, so they must verify the new email/mobile. Once they verify it, this fully activates both the User entity email/mobile that is stored on the User entity as an attribute.
- An existing, authenticated user adds a new email or mobile to their User ID. The email/mobile is stored on the User entity as an attribute with an
activatingstatus. The user then verifies the new email/mobile, and this changes the attribute status toactivated. - An existing, authenticated user updates a current email or mobile with a new one. The replacement email/mobile is stored on the User entity as an attribute with a
pendingstatus. They the user then verifies the replacement new email/mobile.- The old email/mobile attribute is removed from the User entity.
- The new, replacement email/mobile attribute is updated from
pendingtoactivated.
Process Flow - Onboard User
This flow describes the Activate Process at a high level, after it follows the Onboard User with Email and Mobile Process. Preconditions- The User ID (i.e., Storefront Gateway User entity) exists in Storefront Gateway, but the user has not yet verified their email or mobile
- User may be currently anonymous (in Onboarding flows) or authenticated (in Add New Email/Mobile flows).
- Once the user submits their info to Storefront Gateway, they then receive either an email or SMS with an action token (clickable link, OTP, or both).
- The user invokes this Process through one of two methods:
- They manually enter the OTP into client UI (if the client prompts them for a code).
- They click (or tap) the verification link in their email/SMS.
- Storefront Gateway redeems the token, and verifies that the user is coming in from the standard onboarding flow.
- Storefront Gateway verifies the email/mobile and changes the authN ID attribute status from
activatingtoactivated. - Storefront Gateway changes the Storefront Gateway User entity status from
activatingtoactivated. - Storefront Gateway automatically authenticates the user.
- The User is now fully activated.
- The user’s email address or mobile number is now a valid authentication identifier (or authN ID).
- The user can now authenticate with this authN ID and password.
- User not found (i.e., the user ID referenced in the token no longer exists).
- The action token (link or OTP) expired.
Process Flow - Add or Update AuthN ID
This flow describes the Activate Process at a high level, after it follows the Add or Update Email, Mobile, or Alias Process. Note: Aliases are not verifiable. Therefore, they are automatically “activated” as soon as they are created. This Process only applies to email addresses and mobile numbers that users register as authN IDs. Basic Flow- Once the user submits their desired authN ID, they then receive an email or SMS with an action token (clickable link, OTP, or both)
- The user then invokes the Process through one of two methods:
- They manually enter the OTP into client UI (if the client prompts them for a code).
- They click (or tap) the verification link in their email/SMS.
- Storefront Gateway redeems the token, and verifies that the user is coming in from the Add or Update Email, Mobile, or Alias flow.
- Storefront Gateway fully activates a new email/mobile, or updates an existing email/mobile, based on the following criteria:
- The email/mobile currently has a
pendingstatus. This means an existing email/mobile is being updated (as opposed to a new email being added to the User entity). Storefront Gateway changes the email/mobile’s status frompendingtoactivated. If the replaced email/mobile was the user’s primary notification channel, then this setting carries over to the updated email/mobile. - The email/mobile currently has an
activatingstatus. This means it is a new email/mobile being added to the Storefront Gateway User entity. Storefront Gateway changes the new email/mobile’s status fromactivatingstatus toactivated.
- The email/mobile currently has a
- Storefront Gateway changes the Storefront Gateway User entity status from
activatingtoactivated. The following conditions apply:- If a new email/mobile is added to the User ID, then a notification is sent to that new channel.
- If the primary email/mobile was updated, then a notification is also sent to the email/mobile that is being replaced. The notification indicates that this email/mobile that has been removed from Storefront Gateway.
- If the current/primary email or mobile is replaced, then Storefront Gateway invalidates all other sessions (e.g., for remember me/auto-login) except for the current one.
- Storefront Gateway automatically authenticates the user (if they are not already authenticated).
- The new or updated email/mobile is activated as a authentication identifier (authN ID).
- The user can now authenticate with this authN ID and password.
- If a previous email or mobile was replaced, then that email/mobile is removed from the Storefront Gateway User entity.
- User not found (i.e., the user ID referenced in the token no longer exists).
- The action token (link or OTP) expired.
Process Flow - Onboard with Social Account
This flow describes the Activate Process at a high level, after it follows the Onboard (and Authenticate) with Social Account Process. Basic Flow-
(Conditional) Storefront Gateway sends an action token to the user’s email/mobile in one of the following scenarios:
- The user changes the email/mobile value returned by the social provider.
- The social provider does not return an email/mobile. Therefore, the user must provide and verify a contact channel. Note: If the social provider returns an email/mobile, and the user simply confirms that email/mobile, then Storefront Gateway trusts that the provider has validated the contact channel. In that scenario, the Activate User Process is not invoked. Instead, the Onboard & Authenticate User with Social Process completes user activation and authentication.
-
The user then invokes the Process through one of two methods:
- They manually enter the OTP into client UI (if the client prompts them for a code).
- They click (or tap) the verification link in their email/SMS.
- Storefront Gateway redeems the token, and verifies that the user is coming in after the Social Onboarding flow.
- Storefront Gateway registers both the social media ID and email/mobile as attributes on the Storefront Gateway User entity.
- Storefront Gateway automatically authenticates the user (if they are not already authenticated).
- The Storefront Gateway User ID is fully activated and associated to the social account.
- The user can now authenticate with that social account.
- The user-supplied email/mobile is now a valid authentication identifier (or authN ID).
- The user can optionally add a password to their User ID with the Update Password Process.
- User not found (i.e., the user ID referenced in the token no longer exists).
- The action token (link or OTP) expired.
Process Flow - Custom Assistance
A customer calls into the operator’s business call center, and requests help with onboarding. Basic Flow- A customer service representative (CSR) assists a customer over the phone. They enter customer’s first name, last name, and email/mobile in the respective CRM. The following conditions apply:
- The CSR can provide any additional user details to be stored as attributes on the User entity.
- The CSR can not provide a password for the new User entity.
- The CSR can use the Storefront Gateway Care UI to register the new Storefront Gateway User.
- Alternatively, the operator’s proprietary CRM can also invoke one of Storefront Gateway’s REST APIs for User provisioning.
- Storefront Gateway creates the User entity, and stores the authN ID (the user’s email or mobile) as an entity attribute. Both the User entity and the authN ID are created with an
activatingstatus. - Storefront Gateway sends an action token to email/mobile provided by the CSR.
- The user clicks/taps the verification link, and this redirects the user to the client. The following conditions apply:
- The link includes a redirect URL back to the client application, and an action token appended to the end of the URL
- The redirect URL is set in the MarketONE Admin console. Your team will want to build the appropriate landing page, and then set the URL to that landing page in MarketONE Admin.
- The client takes the token from the URL, and uses it to invokes the GET /session/token?={token} API.
- Storefront Gateway looks up and locates the User ID based on the token data.
- Storefront Gateway prompts the user to set a password.
- Storefront Gateway verifies the password, changes both the Storefront Gateway User entity status and authN ID status from
activatingtoactivated. - Storefront Gateway automatically authenticates the user.
App Settings
Certain aspects of the Process’ behavior are controlled by configurable system settings are accessed in the Storefront Gateway Admin console.User Journey Diagram
The Activate User Process comprises the second half of a variety of journeys started with a separate Process. Refer to the User Journey diagrams for these Processes to see where this Process fits into those flows:- Onboard User with Email and Mobile Process
- Onboard and Authenticate User with Social Account Process
- Add/Update Email, Mobile, and Alias Process
Use Cases
See the following use case topics for a guided API walk-through of this Process:- Activate user with one-time passcode (OTP)
- Activate user with verification link (redirect URL)
- Activate user, password required
- Activation errors
- Activate user with an OTP
- Activate user with a verification link
- Activate user, password is required
- Activation Errors