User Authentication with FIDO2 Flow
Preconditions- The User ID exists in Storefront Gateway.
- The user is configured to use FIDO2 to verify their authN ID.
- The user has registered a FIDO2 option.
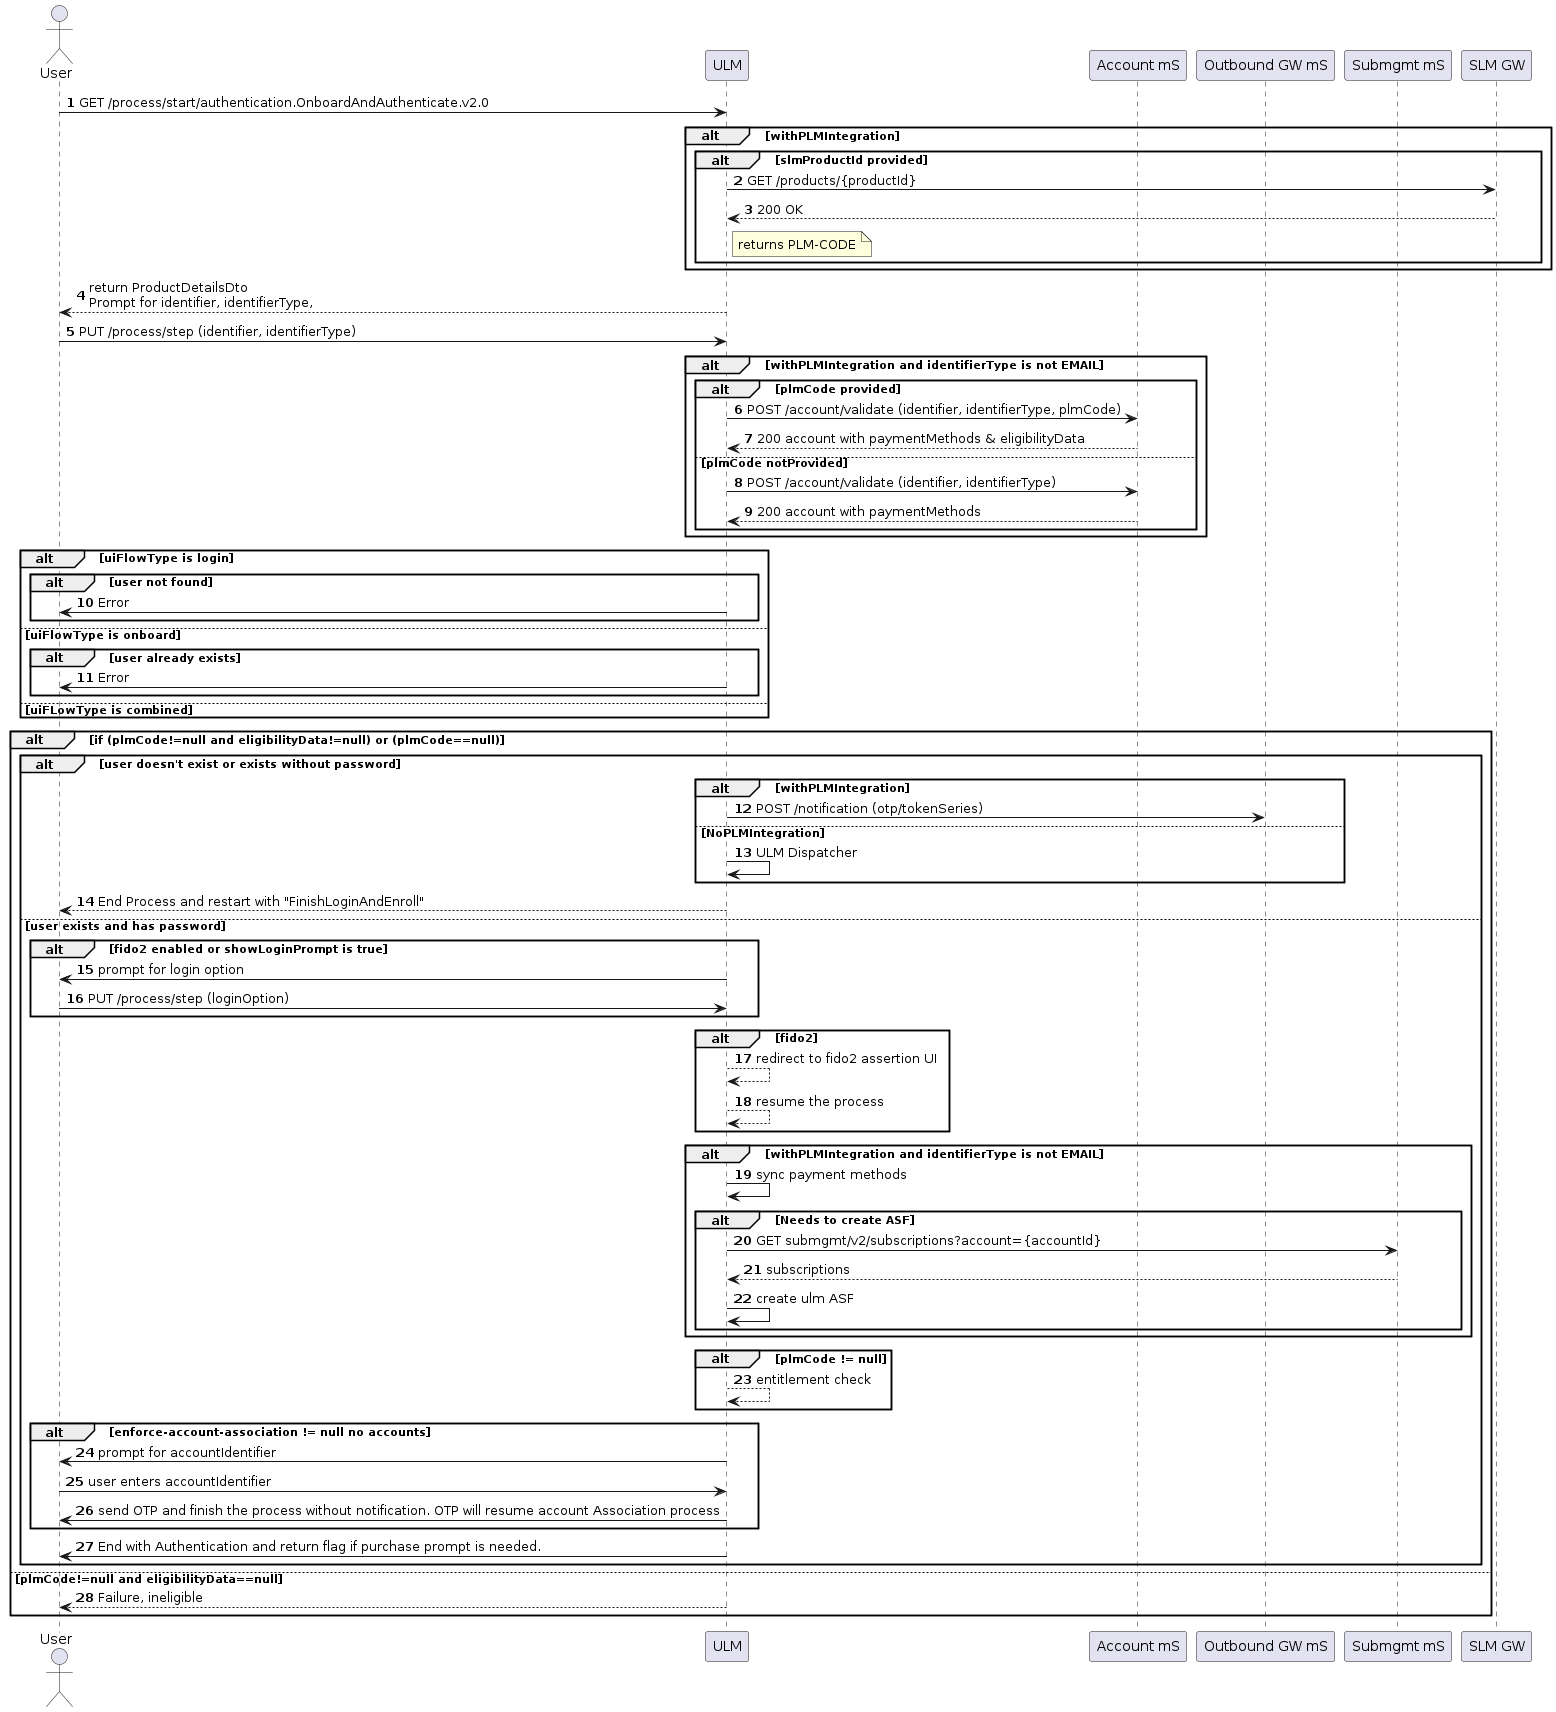
- A user visits the organization’s login page.
- The user logs in with their email/mobile.
- Storefront Gateway redirects user to FIDO2 assertion page to select their option.
- The user enters their FIDO2 credentials. Note: If the user doesn’t have any factors registered for FIDO2, Storefront Gateway guides the user through the onboarding steps to complete their registration and first factor setup.
- The user is logged in after Storefront Gateway’s successful identity verification.
Authenticate User with FIDO2
Application Settings
Some of the relevant app settings for this use case are:showLoginPromptshortTokenExpirationPeriodinMinuteslongTokenExpirationPeriodinMinutes