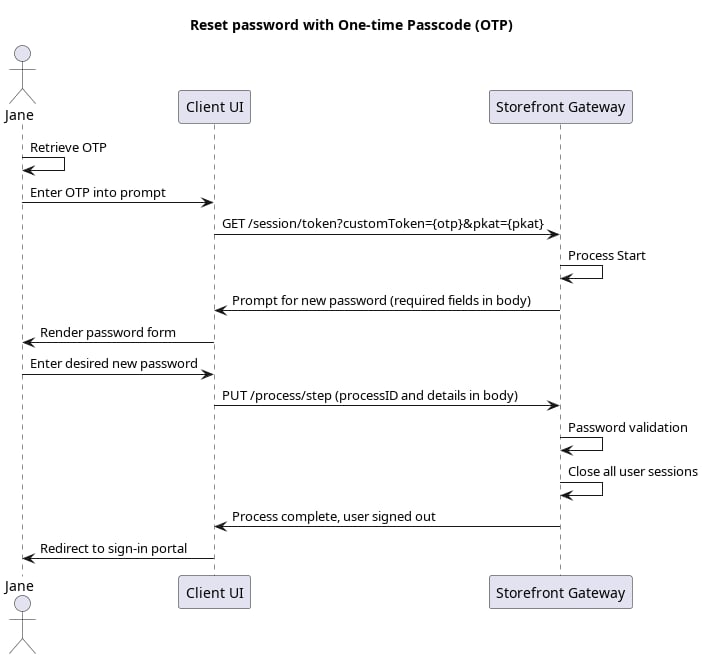
This use case Reset Password Process receives a short code to enter into the next step of the Process flow. This use case is the second half of the “forgot password?” user journey, delivered by the Reset Password Process. In this flow, the user received a short code that they much supply to the Process. An anonymous user has gone through the Recover ID Process, and received an action token in their email or SMS. In this use case, the user receives their action token in the form of a short, custom One-Time Passcode (OTP). The user goes to their email/SMS and retrieves the OTP. They then enter the OTP into the client application. The application passes both the OTP and the Proof Key for Action Token (PKAT) that it received at the end of the previous Process, into the Session Token API:
If both the OTP and PKAT are valid, this API invokes the Reset Password Process.

Response

Storefront Gateway responds with a request for a new password:

Final Request: User Password

Your client calls the Process Step API, and passes the user-supplied password to the Process:

Process Complete

If the password passes complexity rules, then Storefront Gateway replaces the user’s paword. The Process completes and returns a 200 HTTP status:
Storefront Gateway automatically closes any and all open sessions that the user may have. The user will need to sign in with their new password.