- Issue an action token for the Activate User Process, and store the token in the cloud.
- Send a notification to the newly registered email or mobile. The message contains either a verification link, or a verification One-time Passcode (OTP), or both. Note: The verification type (link or OTP) that Storefront Gateway sends is dependent on your organization’s notification settings and notification templates. These settings are configured during your initial onboarding and integration period with Storefront Gateway.
- Return a Proof Key for Action Token (PKAT) to the client application.
Request
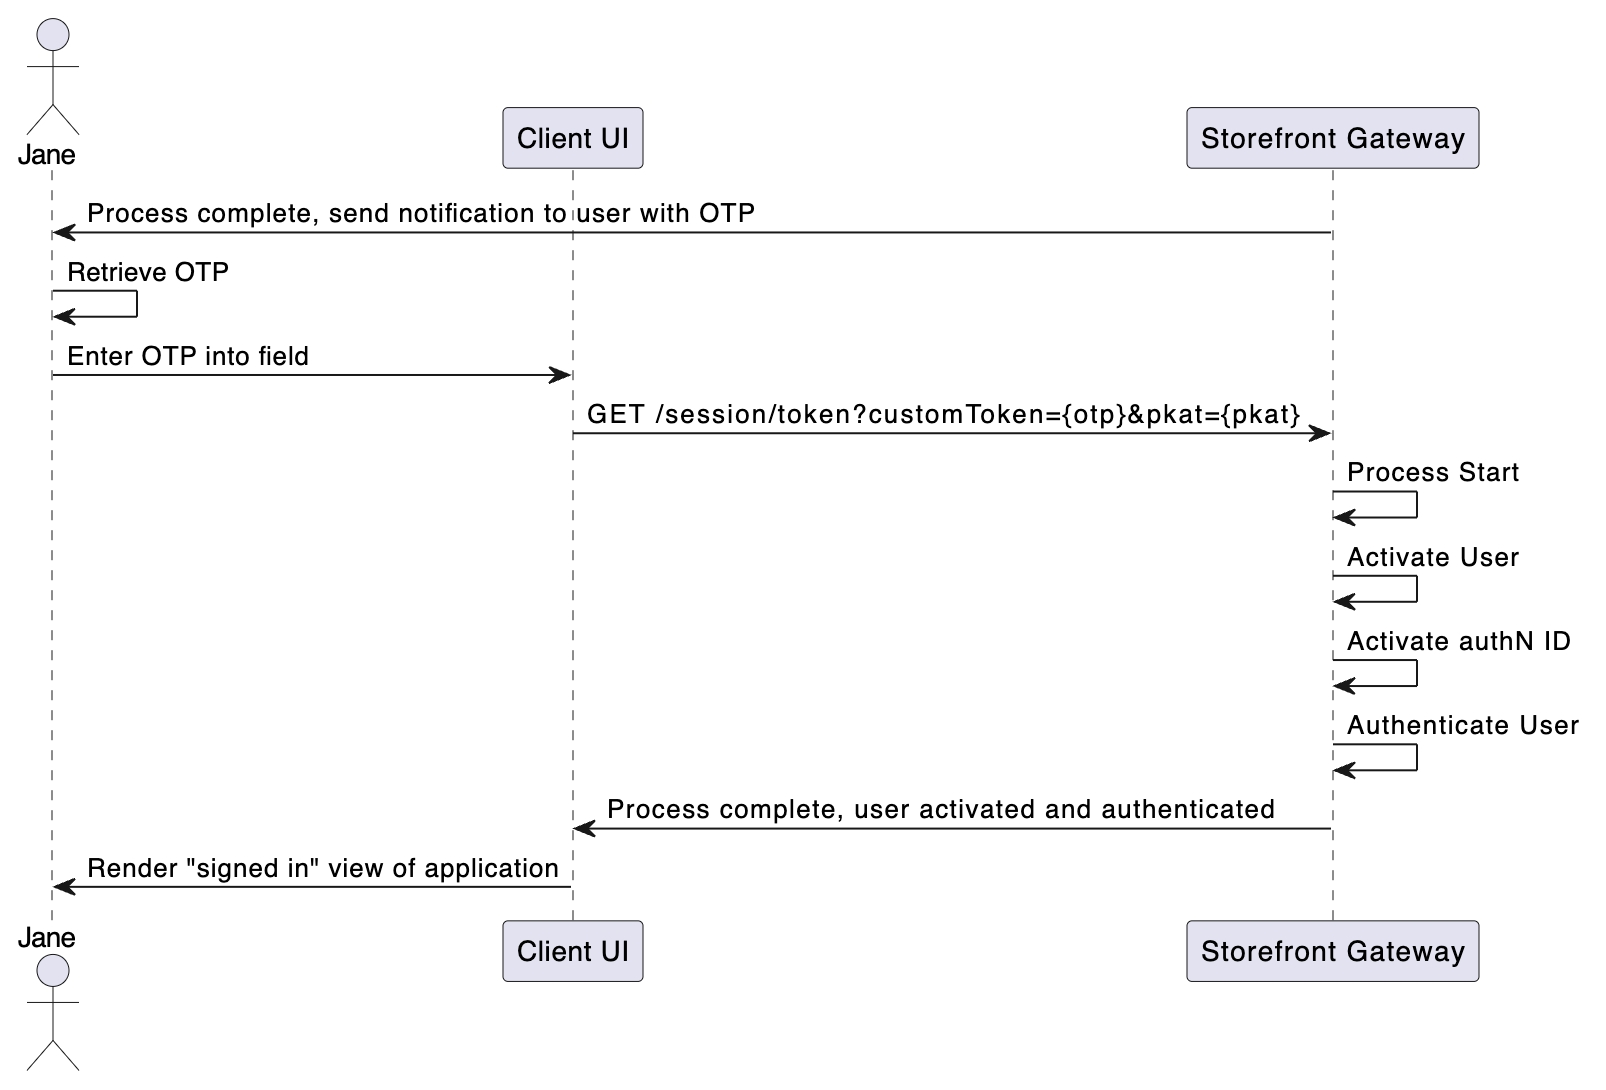
Once the user provides their OTP to your application, the client then calls the Session Token API to invoke the Activate User Process. Your client must supply the OTP and PKAT as URL path parameters:Process Complete
If the token and PKAT are valid, then the Process starts. Storefront Gateway activates the User ID (and user’s authN ID), authenticates the user, and returns a200 HTTP status:
Note: If the user supplies an incorrect OTP three times, then the Session Token API will fail and stop responding. The user would then need to request a verification message resend. They can do this through one of three methods:
- Token Resend API — Resends the same new action token (i.e., the same link). Ideal for use cases where the user is anonymous. Requires the corresponding PKAT.
- Send Verification Process — Issues and sends a new action token (i.e., a new link). Ideal for use cases where the user is authenticated.
- Authenticate User Process — If an end user attempts to sign in with an unverified authN ID, Storefront Gateway will issue and send a new action token. The Process then ends without authenticating the user.